The integrity of patient confidentiality within the NHS has faced a serious breach: fifteen staff members have now been dismissed for unlawfully accessing the medical records of victims from the 2023 Nottingham attack. This incident has raised urgent questions about data security and ethical standards within the health service.
What Happened: Breach of Patient Confidentiality
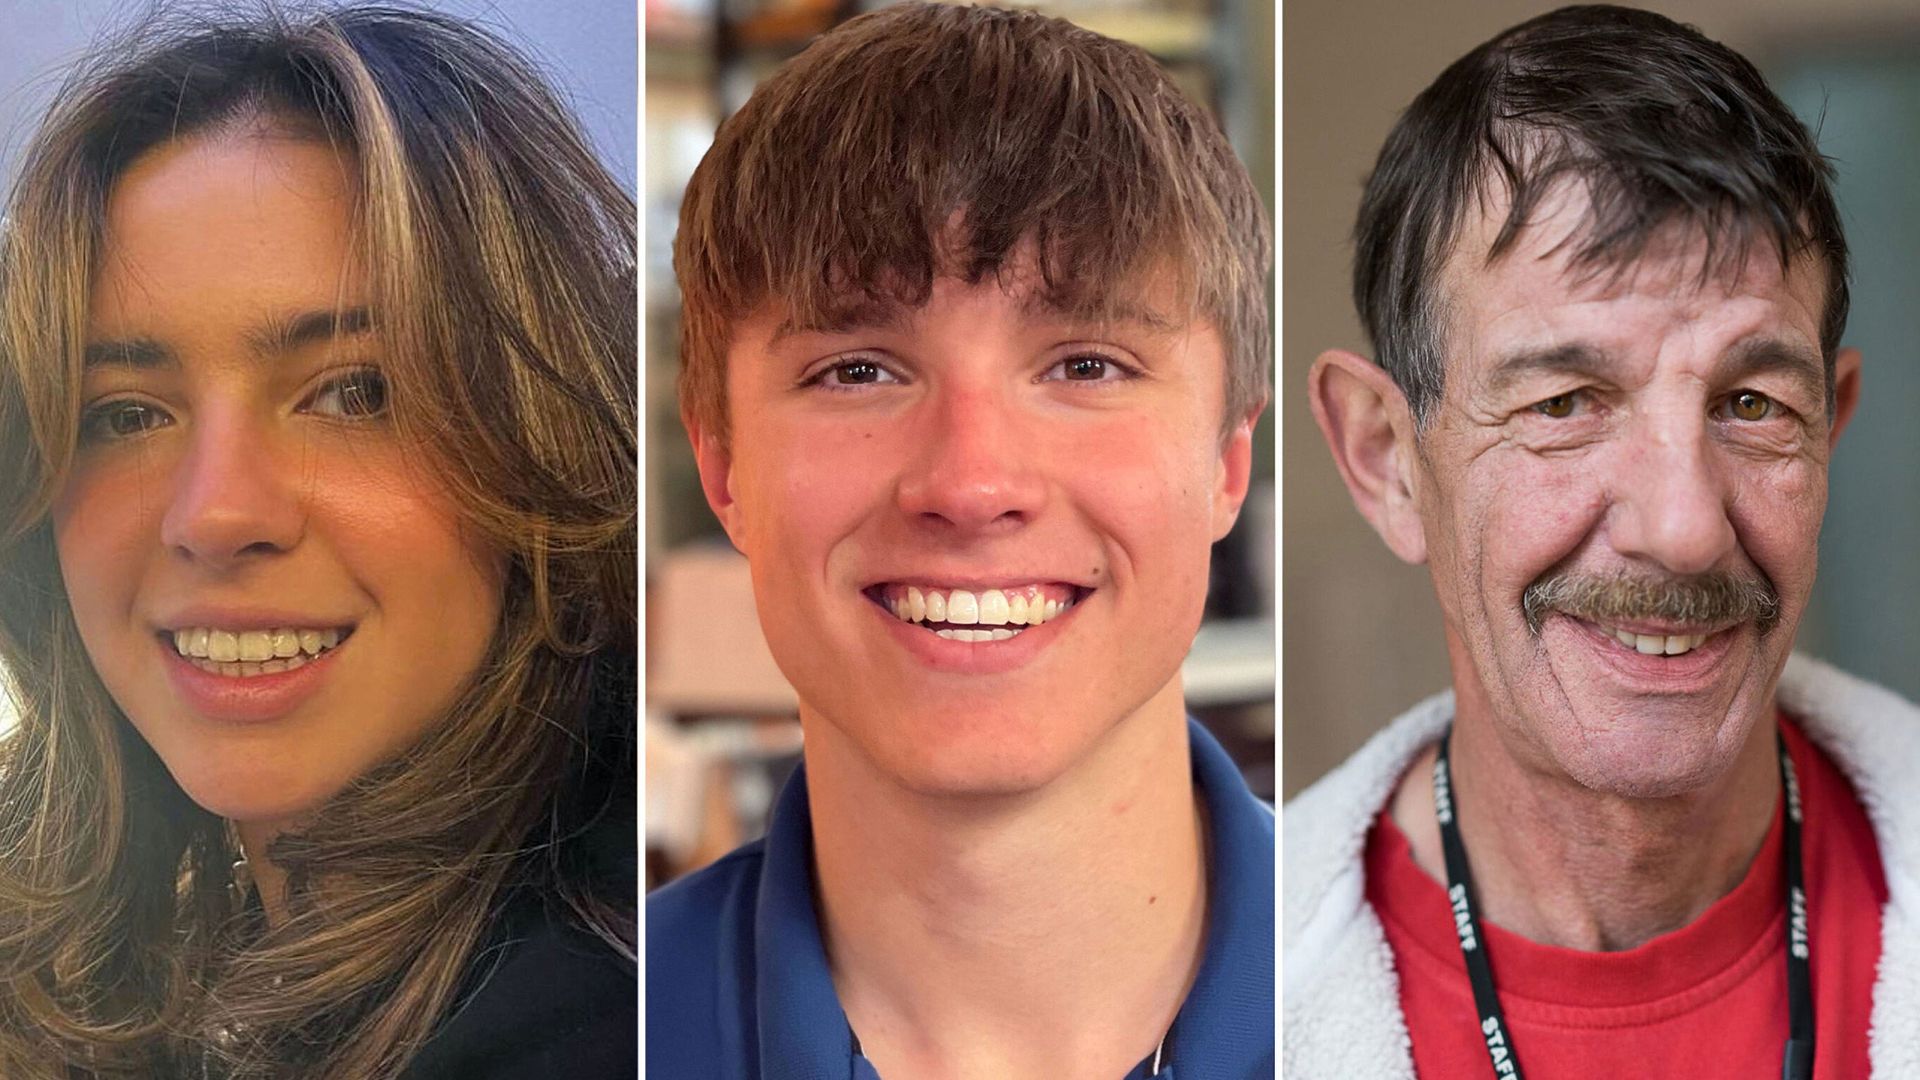
Following the tragic events in Nottingham in 2023, where multiple individuals were injured, it has come to light that numerous NHS employees improperly accessed sensitive medical information related to those victims. This unauthorized access violates strict NHS protocols that protect patient privacy and confidentiality.
The investigation uncovered that a total of fifteen staff members accessed these records without any legitimate medical reason or patient consent. As a result, all fifteen individuals have been formally sacked from their positions within the NHS. Confidentiality breaches of this nature not only undermine trust in healthcare providers but may also have legal ramifications for the staff involved and the health service overall.
Why This Matters: Upholding Trust and Data Security in Healthcare
The NHS holds an immense responsibility to safeguard patient data. Medical records contain highly sensitive information, and unauthorized access can cause significant distress to patients and families, especially in cases involving trauma such as the Nottingham attack.
Security protocols are designed to ensure that only authorized personnel involved in direct patient care can access such details. Breaches erode public confidence in the system, potentially deterring individuals from seeking medical help or sharing crucial information with healthcare providers.
Moreover, these incidents highlight the ongoing challenges faced by large institutions in protecting digital information. As medical records increasingly move to electronic systems, the risk of unauthorized access grows, emphasizing the need for robust monitoring and enforcement mechanisms.
What Comes Next: Strengthening Protections and Accountability
The dismissal of these fifteen staff members sends a clear message that violations of patient confidentiality will not be tolerated within the NHS. However, this event should also prompt a broader review of data governance policies and staff training programs across healthcare trusts.
Healthcare organisations must ensure that all personnel understand the gravity of data privacy laws and the ethical imperatives tied to patient information. Regular audits, improved access controls, and swift disciplinary actions are essential tools to prevent future breaches.
Furthermore, transparency about such incidents and their consequences is vital to maintaining public trust. Patients deserve reassurance that their information is handled with the utmost care and that any misuse is promptly addressed.
Looking Ahead: A Renewed Commitment to Patient Privacy
The Nottingham attack was a tragic event that deeply affected many lives. The subsequent misuse of victims’ medical records adds an additional layer of harm that the NHS must work hard to rectify. By taking decisive action against those responsible and reinforcing data security measures, the NHS can begin to rebuild trust and demonstrate its commitment to protecting patient confidentiality.
As healthcare continues to evolve in the digital age, safeguarding sensitive information remains paramount. This episode underscores the importance of vigilance, accountability, and respect for patient rights within the NHS and beyond.